TRUSTED BY


PCI DSS Level 1
Protection for Merchants
Outsource your card security compliance burden to PhonePe and focus on growing your core business.
Level 1 Certification
Certified under the highest global standard for payment card industry security.
Zero-Card Vaulting Burden
Offload card data storage risks entirely—PhonePe securely handles all cardholder details.
Secure Channels
Transmit payment data over ultra-secure, encrypted network channels.
Regular Vulnerability Audits
Undergo rigorous quarterly network scans and annual third-party security audits.
Frictionless and
Compliant Checkout
Protect your brand reputation and eliminate compliance liabilities with certified card processing.
RBI & Global Alignment
Fully aligned with RBI payment regulations and international card network standards.
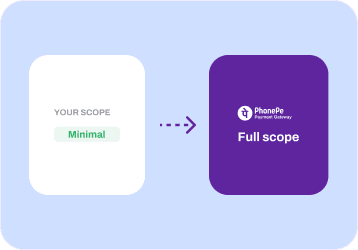
Reduced Audit Scope
Minimize your own PCI compliance requirements by routing card payments through our secure checkout.
Fraud Prevention Guarantee
Shield your checkout from card-not-present fraud with 3D Secure 2.0 authentication.
Transparent Security Reporting
Access compliance documentation and SOC reports easily whenever required.
Trusted by
India's Largest Online Brands
Trusted by India's
Largest Online Brands
"In E-commerce, the right Payment Gateway partnership is crucial. PhonePe PG streamlined our Payments, & reduced cart abandonment. PhonePe PG exceeded our expectations with a top-notch product & impeccable support.”
Suman Patra
Co-founder
"redBus is committed to redefining travel through technology. Collaborating with PhonePe PG allows us to leverage their robust Payment infrastructure, ensuring reliability and innovation for millions of our customers.”
Rithish Saralaya
SVP Engineering
"Our partnership with PhonePe Payment Gateway has been seamless and highly efficient. Their robust tech, smooth integration, & reliable support played a key role in enhancing our customer experience. We truly value this collaboration.”
Vikash Goyal
CSO
"As GIVA expands, a trusted Payment partner at every touchpoint is vital. PhonePe PG offers us reliability across our national stores and on our app. Their support scales with our growth, and that consistency makes all the difference for us.”
Ishendra Agarwal
Founder
"Our partnership with PhonePe PG has been a pivotal factor in our success story. With PhonePe PG's user-friendly interface and seamless Payment processing, we can continue delivering exceptional service to our valued customers.”
Ritu Shah & Minita Parekh
Co-founders

"Partnering with PhonePe Payment Gateway enabled us to expand our D2C business and transform period care across India. Its seamless integration and dependable partner support means our online customers' experience lives up to our brand's Zero Irritation promise.”
Ravi Ramachandran
Co-Founder & CEO
Comprehensive Solutions
Comprehensive
Solutions
To keep your Business Ahead of the Rest
Automate flexible subscriptions for steady cash flow.
Faster, error-free checkouts using tokenized cards boost revenue.
Accept International Payments, simplify growth.
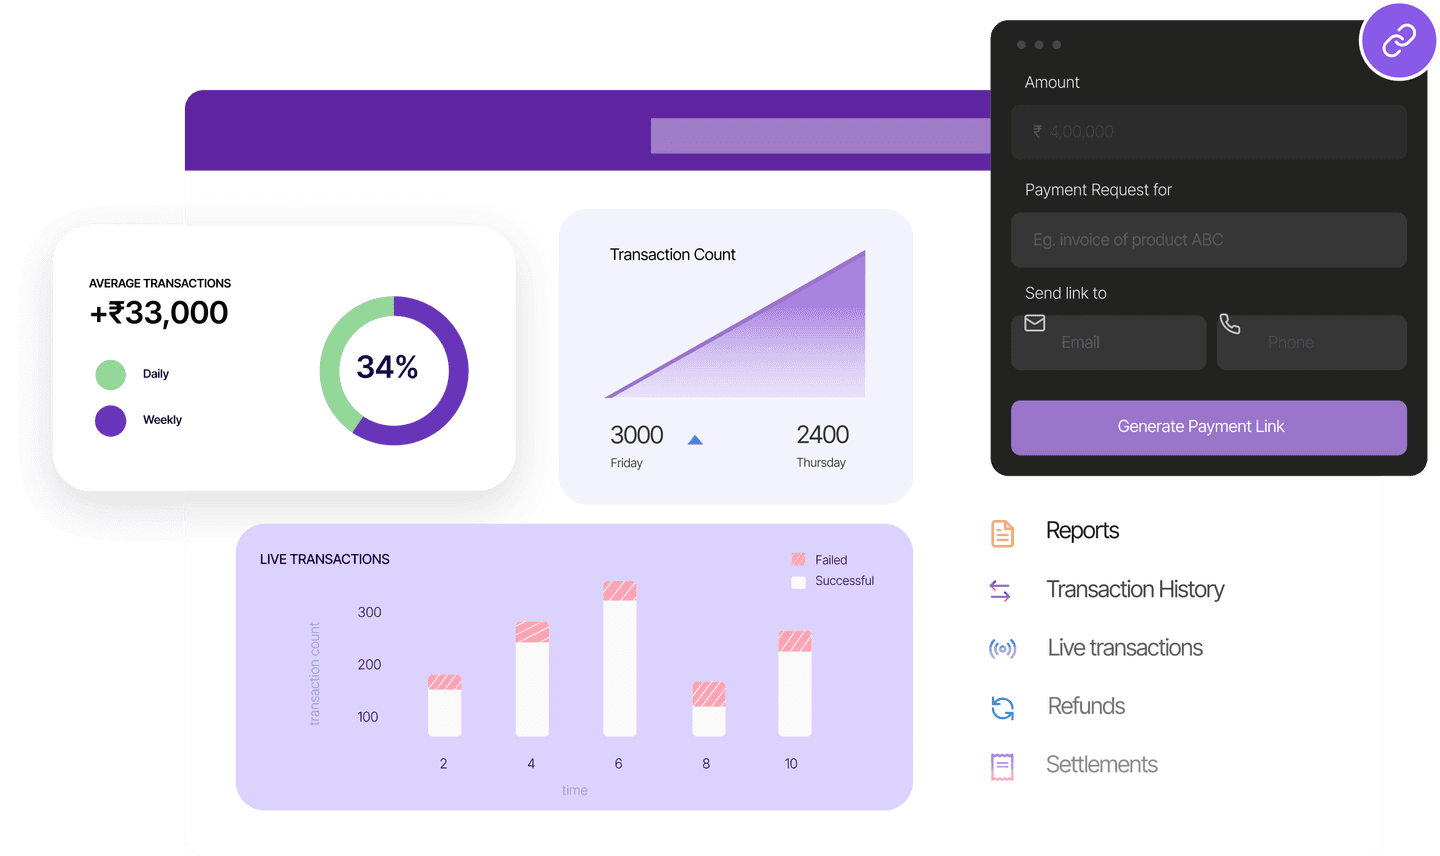
Send Payment links (WhatsApp/SMS/Email), get paid instantly

Dynamic QR codes enable UPI, reducing errors and boosting success.
Digital doorstep Payments replace COD, cutting cash handling costs.



PCI DSS Compliance FAQs
What level of PCI DSS certification does PhonePe PG hold?
PhonePe PG is certified as a PCI DSS (Payment Card Industry Data Security Standard) Level 1 Service Provider the highest level of certification awarded in the payment industry. This certification verifies that PhonePe's infrastructure, network, and data handling practices meet stringent global security benchmarks for processing millions of card transactions safely.
How does integrating PhonePe PG reduce my business's PCI DSS compliance scope?
When you use PhonePe's Hosted Checkout, Mobile SDKs, or iFrames, cardholder data is submitted directly to PhonePe’s compliant servers. Because card numbers, CVVs, and expiry dates never touch, process, or store on your own application servers, your PCI audit scope is reduced to the simplest level, allowing you to qualify for a streamlined Self-Assessment Questionnaire.
Do I need my own PCI DSS certification to accept card payments via PhonePe PG?
If you use standard Hosted Payment Pages, Payment Links, or PhonePe’s pre-built SDKs, you do not need an independent PCI DSS audit. However, if you opt for a custom Direct API (Server-to-Server) integration where customer card credentials are collected directly on your site's form before being transmitted, your business must obtain and maintain its own PCI DSS compliance.
How does PhonePe's tokenization process support PCI DSS requirements?
In compliance with RBI mandates and PCI DSS standards, PhonePe PG uses Card-on-File Tokenization (CoFT). Raw 16-digit card numbers are swapped for unique, encrypted network tokens issued by Visa, Mastercard, or RuPay. This allows repeat customers to save cards for seamless 1-click checkouts without exposing raw card details to breach risks.
What level of PCI DSS certification does PhonePe PG hold?
PhonePe PG is certified as a PCI DSS (Payment Card Industry Data Security Standard) Level 1 Service Provider the highest level of certification awarded in the payment industry. This certification verifies that PhonePe's infrastructure, network, and data handling practices meet stringent global security benchmarks for processing millions of card transactions safely.