TRUSTED BY


Safeguarding
Merchant Data
We enforce strict data handling policies to ensure merchant and customer information remains confidential and secure.
Data Minimization Principle
We collect only the essential data required to process payment transactions successfully.
DPDP Act Compliance
Fully compliant with Digital Personal Data Protection laws and Indian regulatory standards.
Strict Data Ownership
Your customer data belongs exclusively to you; we never sell or share data with third parties.
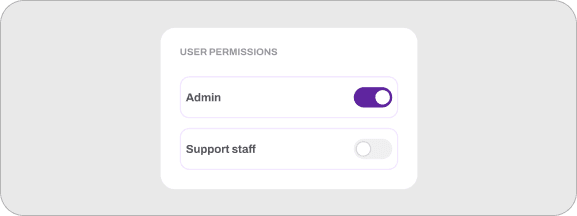
Granular Privacy Controls
Easily manage user permissions and access levels within your merchant dashboard.
Responsible
Data Management
Experience full transparency in how payment data is collected, processed, stored, and retained.
Secure Local Data Residency
Store and process all financial and customer data strictly on servers within India.
Encrypted Storage Vaults
Safeguard all stored customer logs and profiles behind multi-layered encryption.
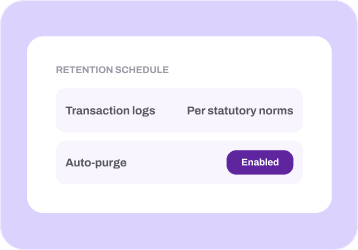
Clear Data Retention Timelines
Retain transaction logs strictly according to statutory financial guidelines.
Instant Privacy Support
Dedicated data protection officers to address privacy inquiries and data requests swiftly.
Trusted by
India's Largest Online Brands
Trusted by India's
Largest Online Brands
"In E-commerce, the right Payment Gateway partnership is crucial. PhonePe PG streamlined our Payments, & reduced cart abandonment. PhonePe PG exceeded our expectations with a top-notch product & impeccable support.”
Suman Patra
Co-founder
"redBus is committed to redefining travel through technology. Collaborating with PhonePe PG allows us to leverage their robust Payment infrastructure, ensuring reliability and innovation for millions of our customers.”
Rithish Saralaya
SVP Engineering
"Our partnership with PhonePe Payment Gateway has been seamless and highly efficient. Their robust tech, smooth integration, & reliable support played a key role in enhancing our customer experience. We truly value this collaboration.”
Vikash Goyal
CSO
"As GIVA expands, a trusted Payment partner at every touchpoint is vital. PhonePe PG offers us reliability across our national stores and on our app. Their support scales with our growth, and that consistency makes all the difference for us.”
Ishendra Agarwal
Founder
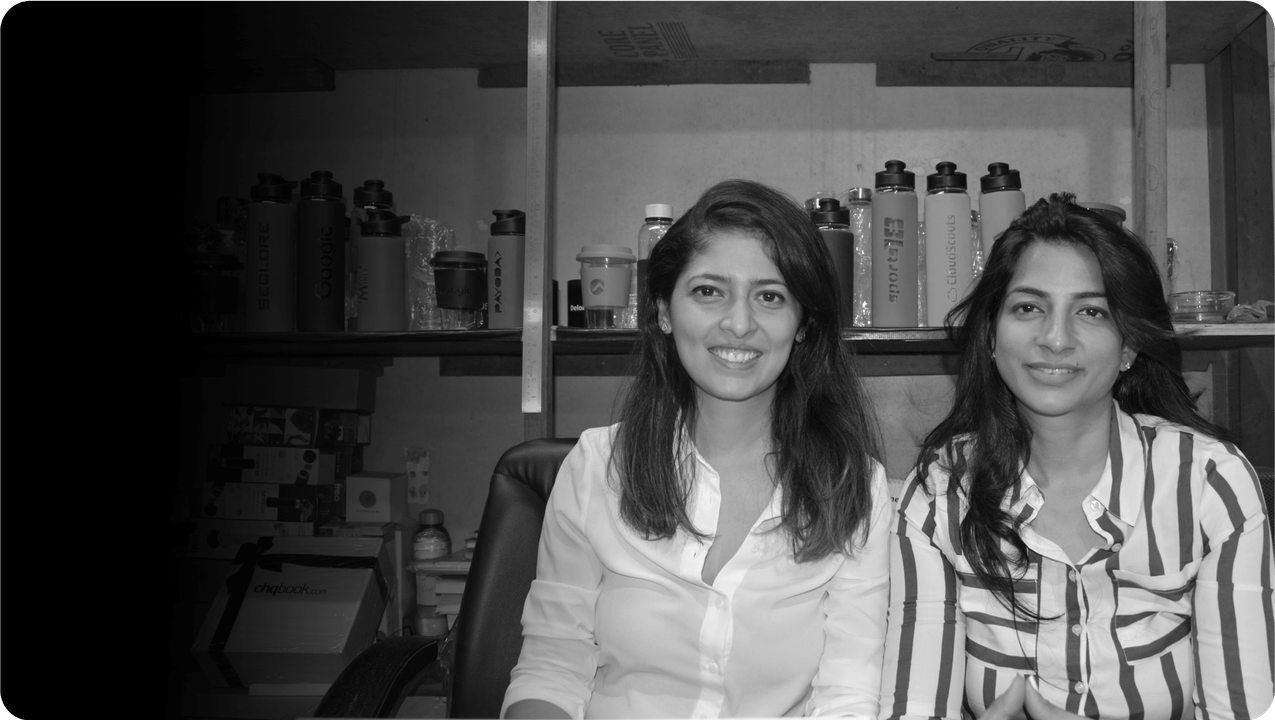
"Our partnership with PhonePe PG has been a pivotal factor in our success story. With PhonePe PG's user-friendly interface and seamless Payment processing, we can continue delivering exceptional service to our valued customers.”
Ritu Shah & Minita Parekh
Co-founders

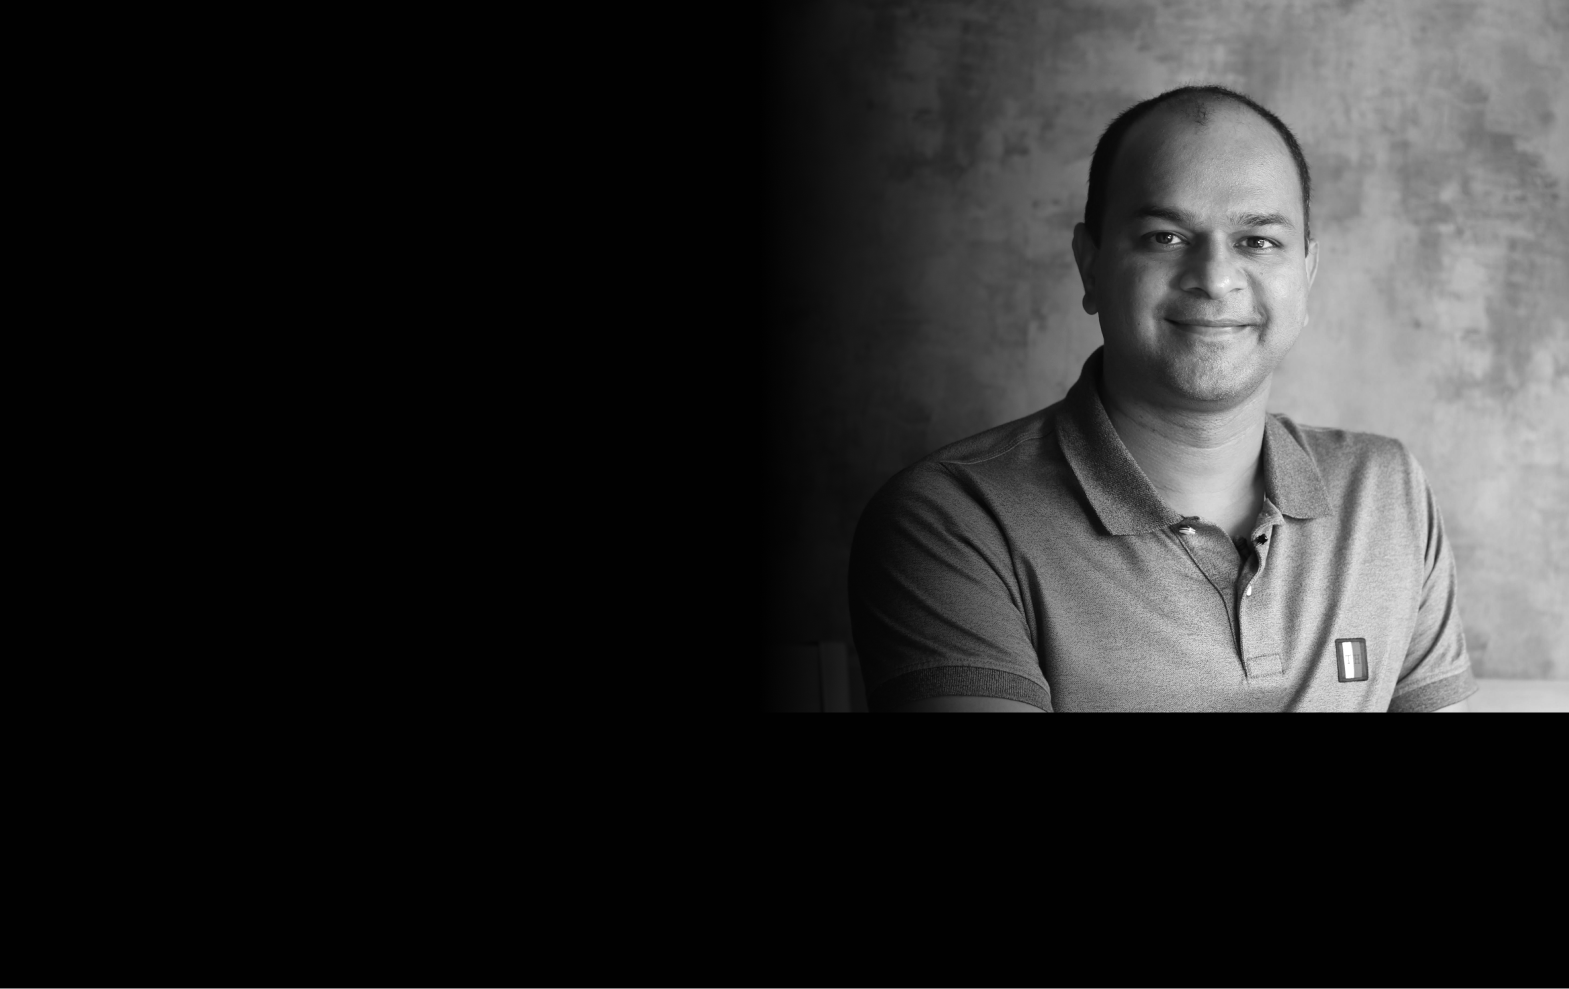
"Partnering with PhonePe Payment Gateway enabled us to expand our D2C business and transform period care across India. Its seamless integration and dependable partner support means our online customers' experience lives up to our brand's Zero Irritation promise.”
Ravi Ramachandran
Co-Founder & CEO
Comprehensive Solutions
Comprehensive
Solutions
To keep your Business Ahead of the Rest
Automate flexible subscriptions for steady cash flow.
Faster, error-free checkouts using tokenized cards boost revenue.
Accept International Payments, simplify growth.
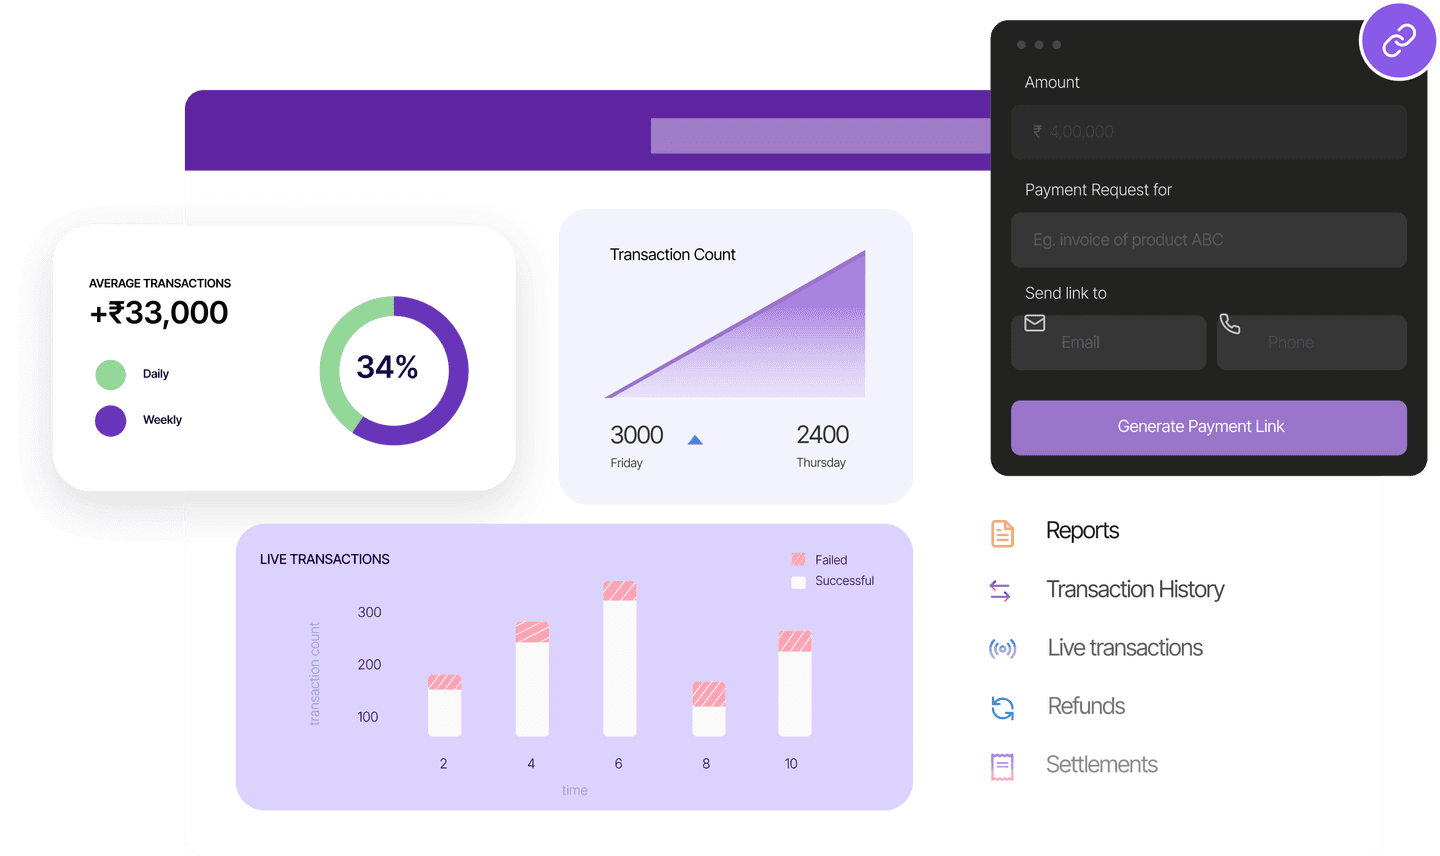
Send Payment links (WhatsApp/SMS/Email), get paid instantly

Dynamic QR codes enable UPI, reducing errors and boosting success.
Digital doorstep Payments replace COD, cutting cash handling costs.



Data Protection FAQs
Where is customer transaction and payment data stored by PhonePe PG?
In accordance with Reserve Bank of India (RBI) data localization mandates and the Digital Personal Data Protection (DPDP) Act, PhonePe PG stores all payment records, customer transaction history, and system logs exclusively within data centers located in India. No customer payment credentials or personal information are transferred to or processed on overseas servers.
How does PhonePe PG handle customer consent for data processing?
PhonePe PG processes personal and financial data based on explicit consent flows. In compliance with Indian data protection regulations, data collection is restricted to necessary information—such as phone numbers, masked payment details, and device identifiers—needed strictly to facilitate transaction completion, fraud prevention, and regulatory reporting.
Can merchants access or store raw customer payment details?
No. PhonePe PG strictly enforces data minimization. Merchants are only provided with essential transaction metadata, such as unique order IDs, status codes, and masked instrument details (e.g., the last four digits of a card or a masked UPI ID). Raw credit/debit card numbers, CVVs, and banking credentials are kept isolated within PhonePe's PCI-compliant environment and are never shared with merchants.
How does PhonePe PG ensure data privacy during third-party integrations?
Integrations with partner banks, card networks, and identity verification services operate under strict Data Processing Agreements (DPAs). All data transfers occur over TLS-encrypted APIs, and third parties are permitted to process information solely for payment authorization, clearing, and statutory compliance without retaining unauthorized copies.
Where is customer transaction and payment data stored by PhonePe PG?
In accordance with Reserve Bank of India (RBI) data localization mandates and the Digital Personal Data Protection (DPDP) Act, PhonePe PG stores all payment records, customer transaction history, and system logs exclusively within data centers located in India. No customer payment credentials or personal information are transferred to or processed on overseas servers.